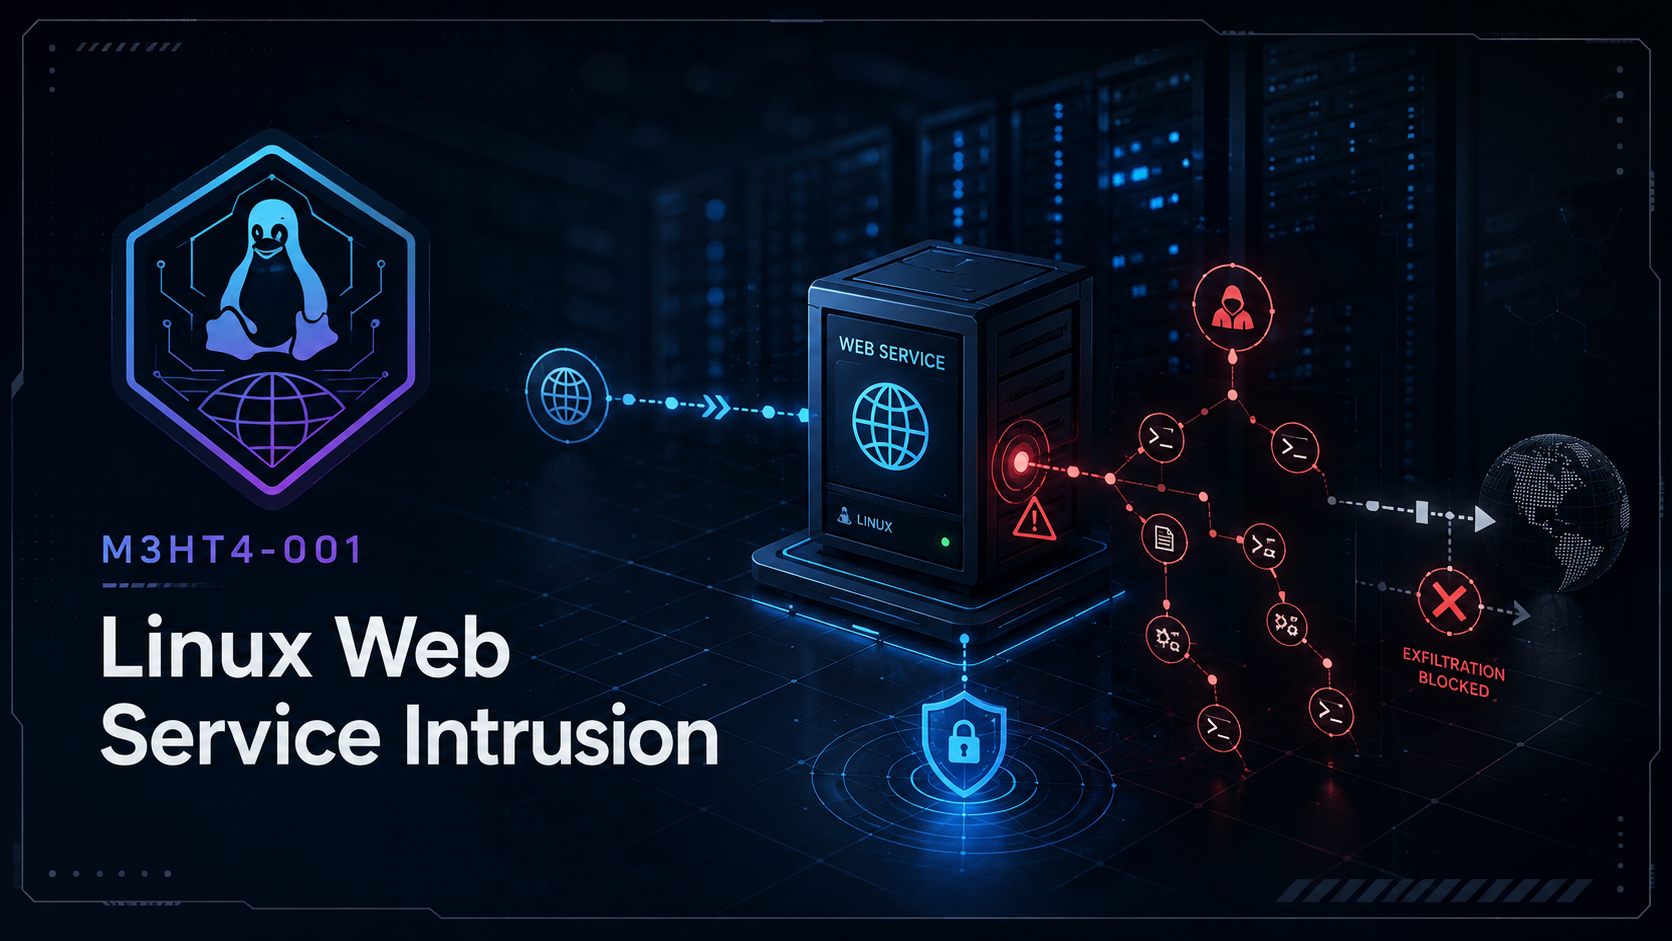
Linux Web Service Intrusion
Contained before exfiltrationFollow a public-facing Linux service compromise through shell execution, discovery, collection, represented command-and-control, detection, and containment.
Explore a functional preview of the M3HT4 replay experience. Every event, host, process, artifact, and finding on this page is synthetic and runs entirely in your browser.
Each replay follows the same M3HT4 learning model: trace the behavior, inspect the evidence, switch team lenses, and understand how detection and validation connect across the attack path.
Follow a public-facing Linux service compromise through shell execution, discovery, collection, represented command-and-control, detection, and containment.
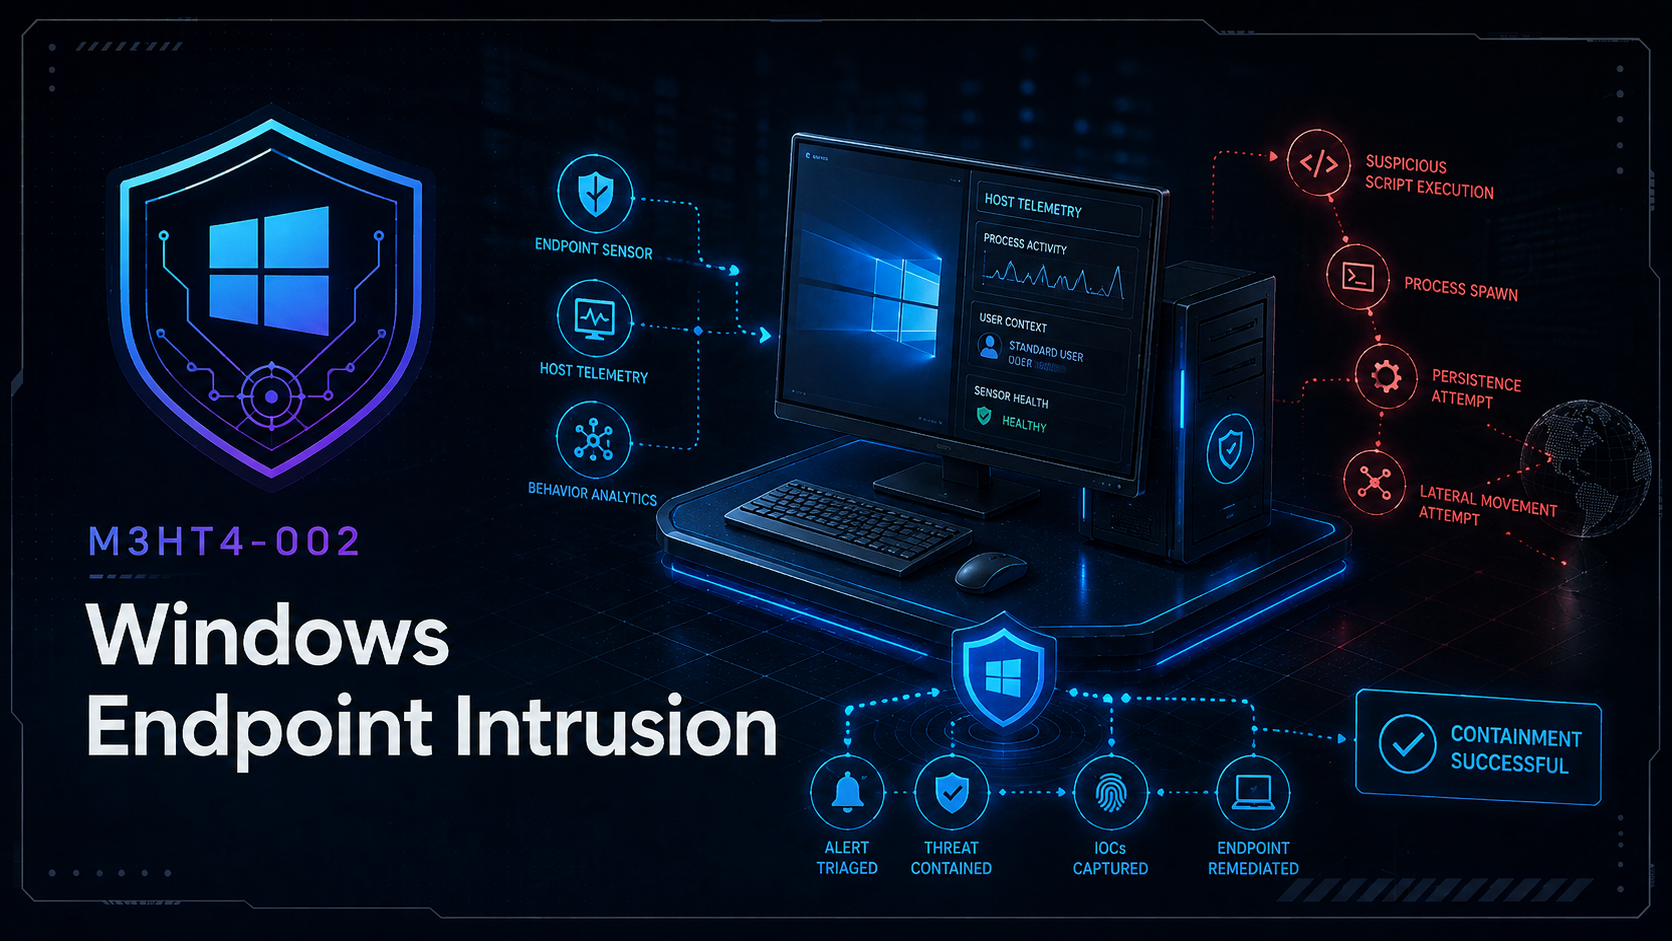
A planned Windows replay centered on process ancestry, endpoint telemetry, persistence signals, investigation, and containment.
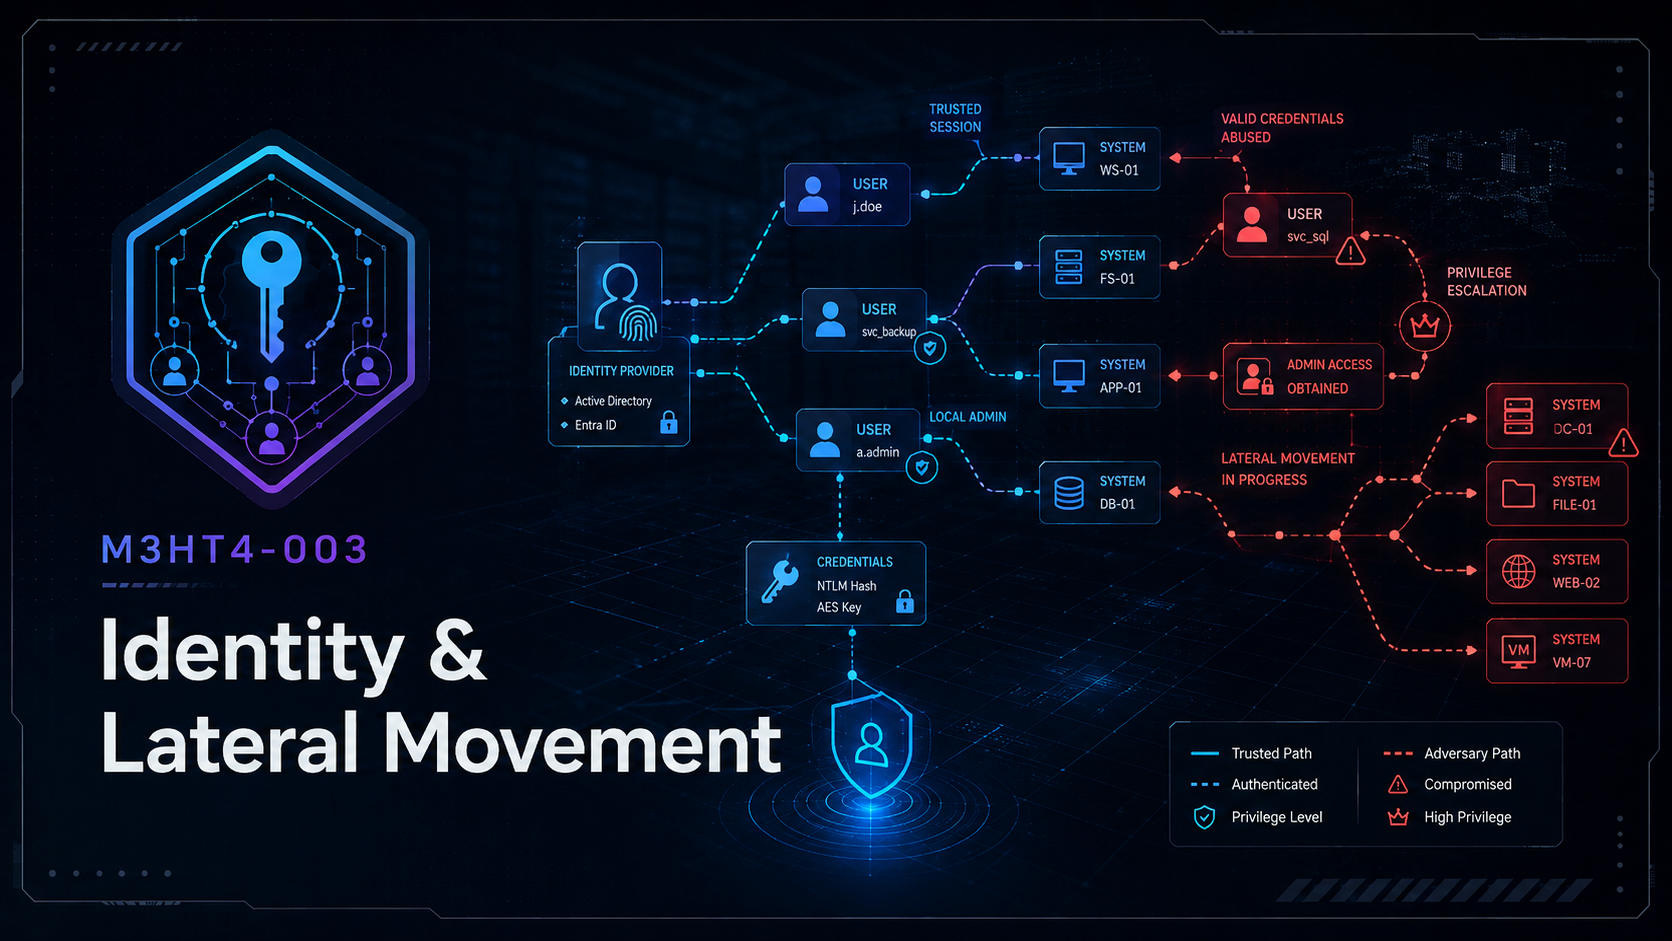
A planned identity replay connecting authentication evidence, credential-use anomalies, host relationships, movement, and detection coverage.
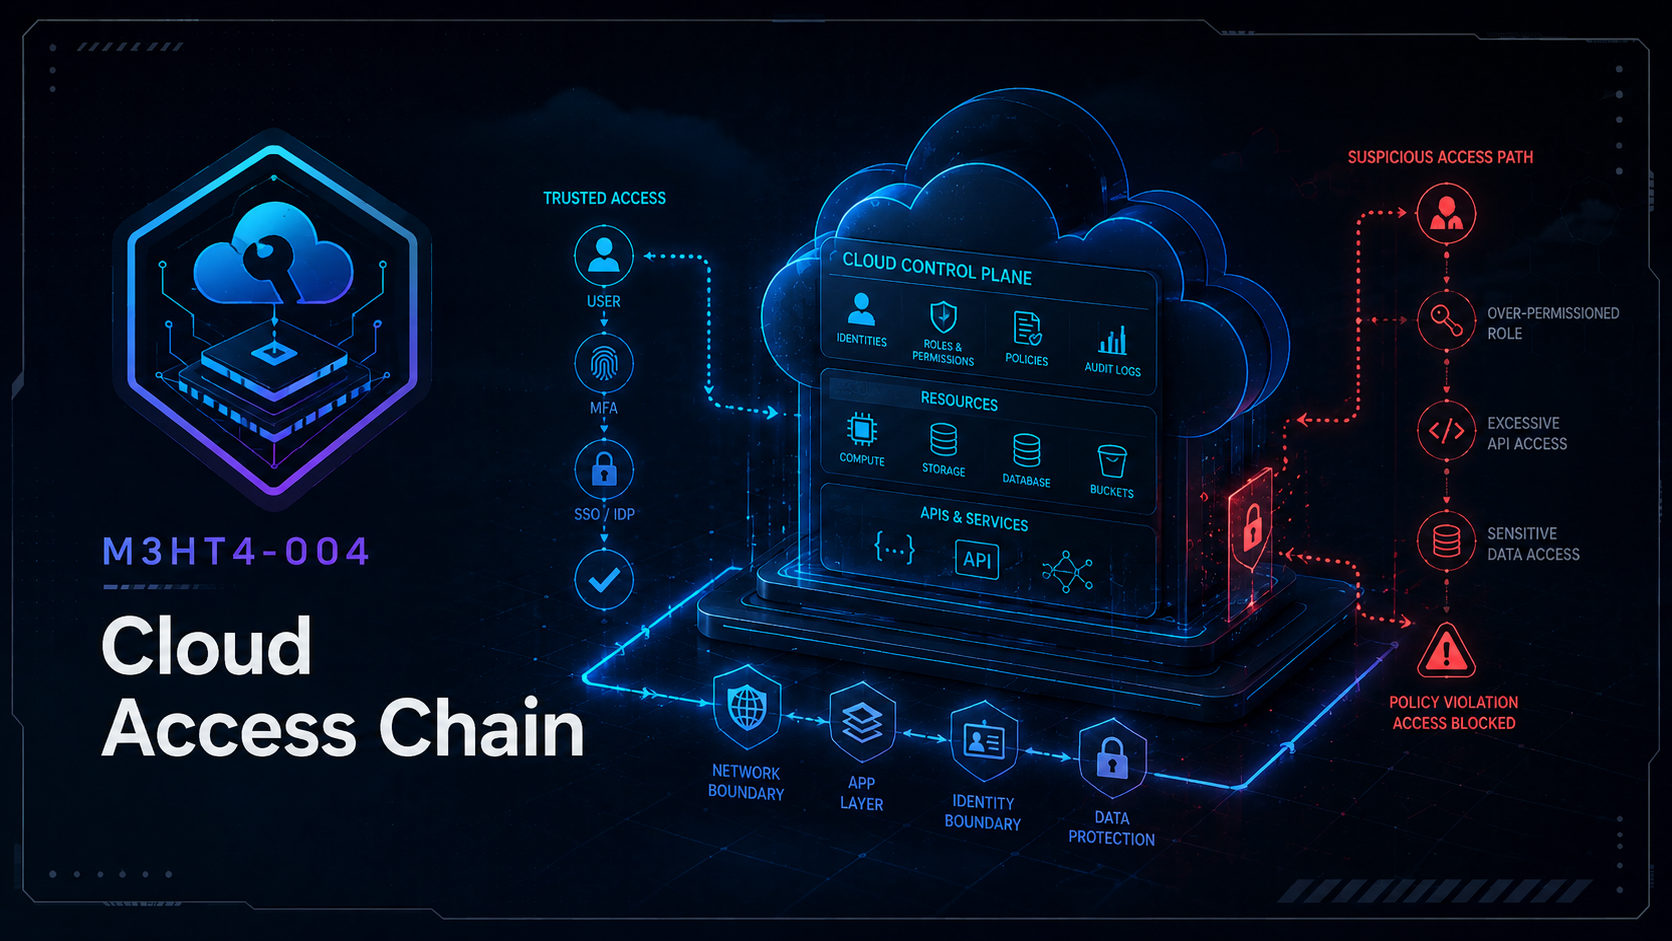
A future cloud replay showing how identity and control-plane events connect across Red intent, Blue investigation, and Purple validation.
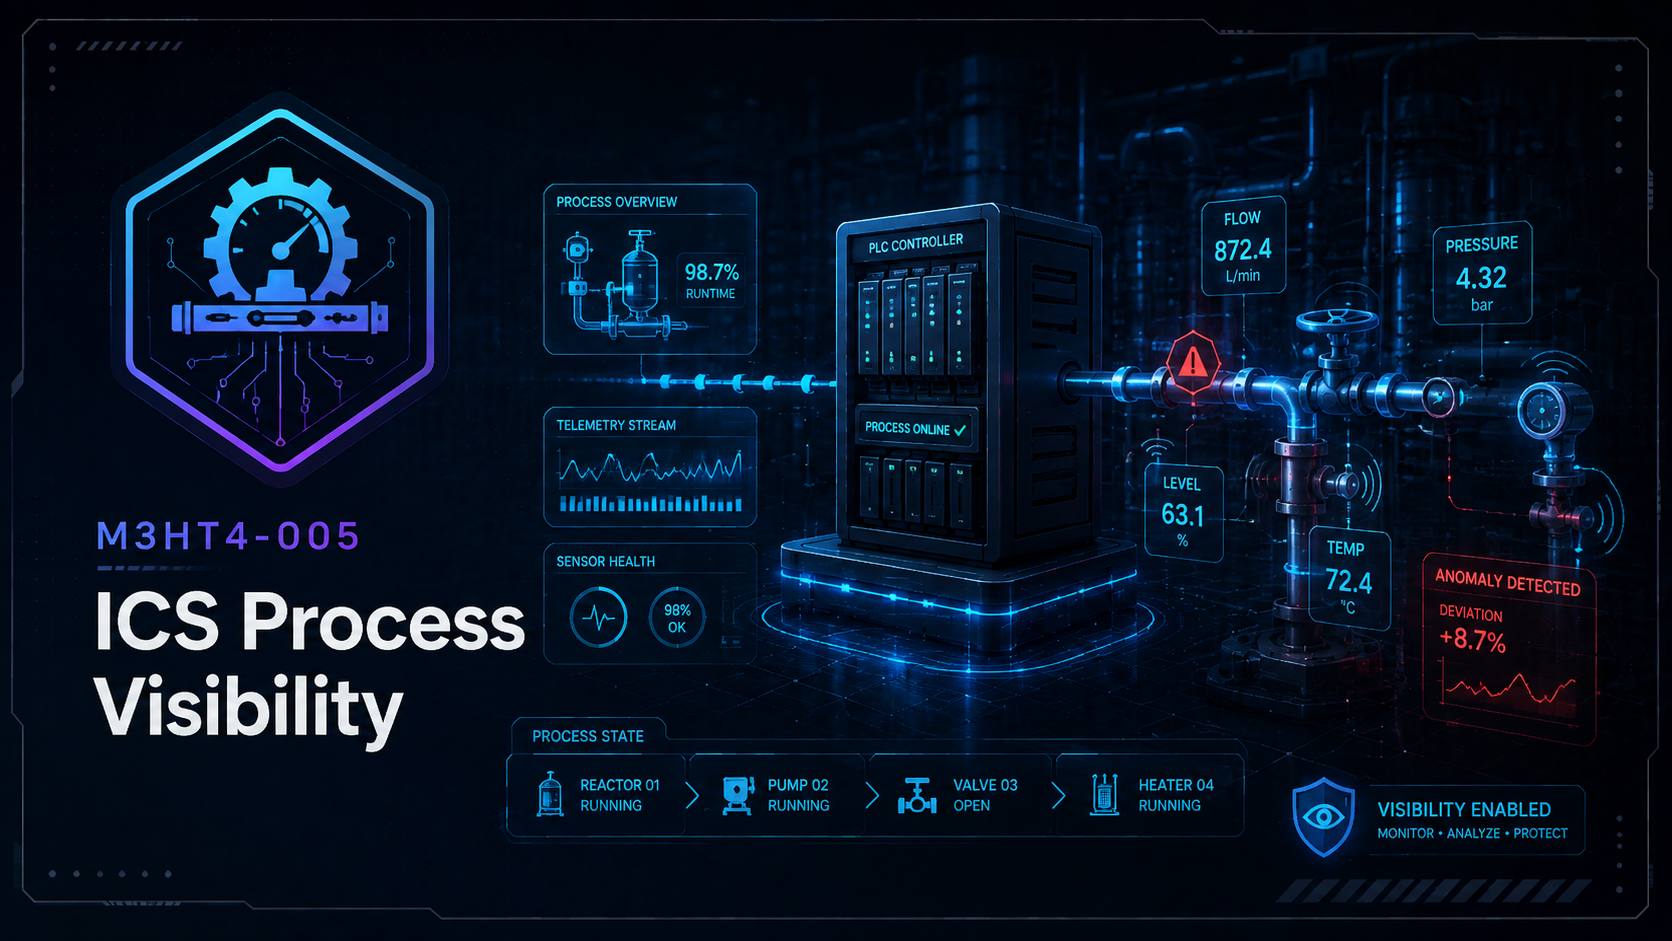
A future isolated ICS replay focused on safe process visibility, network telemetry, defender context, and Purple validation.
The catalog is separate from the replay engine. New scenarios can be added here without redesigning the Platform; later we can add search, filters, collections, difficulty tracks, and dedicated scenario pages.
This beta is a static client-side simulation. It cannot execute commands, accept uploads, access the private M3HT4 lab, reach management interfaces, or retrieve live telemetry. The network example uses the documentation-only TEST-NET-2 address range.
Read the M3HT4 Responsible Use & Research Policy →